English
 Deutsch
 Polski
Safari ITP, CNAME Cloaking, and the Challenges of First-Party Tracking

Contents
A subdomain of the website does not guarantee persistent analytics cookies. Safari can limit cookies from HTTP responses when the endpoint is recognised as a cloaked third party. A useful assessment separates the setting method, DNS destination, browsing mode and stored expiry.
1. What CNAME cloaking means
A CNAME makes one hostname an alias of another: data.example.com might point to collector.vendor.example. The browser still requests the first name. Tracking infrastructure operated elsewhere can consequently appear under the visited website’s subdomain. CNAME records also serve ordinary hosting purposes; their presence alone does not prove tracking.
WebKit describes detection through the DNS relationship to the website and the top-level document’s CNAME. This is a technical rule, not a check of company ownership. Cookie domain and actual DNS destination are therefore separate inspection points.
2. Distinguishing seven-day and 24-hour rules
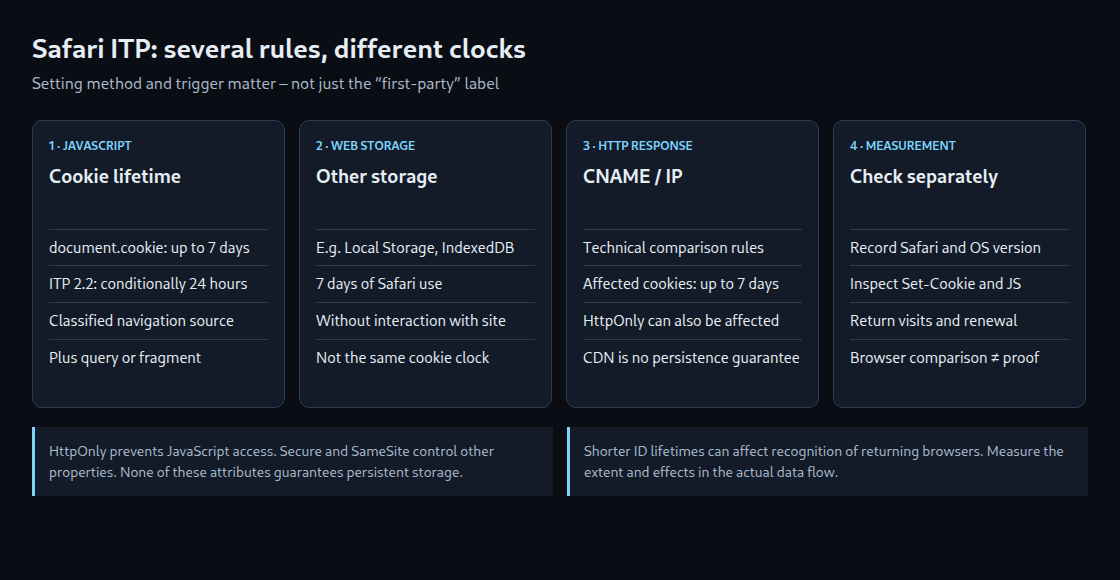
- JavaScript cookies: ITP 2.1 introduced a seven-day expiry cap for persistent cookies created through
document.cookie. A shorter declared expiry remains shorter. - Link decoration: ITP 2.2 describes a one-day cap for these cookies on the landing page when a domain classified for cross-site tracking initiated navigation and the destination URL has a query string or fragment. A single
utm_sourceparameter does not establish that combination. - Other browser storage: The 2020 removal rule for script-writable data such as LocalStorage and IndexedDB counts seven days of Safari use without interaction with the website. This differs from capping a cookie’s expiry timestamp.
- CNAME/IP cloaking: When a cloaked third-party endpoint is detected, cookies set by the HTTP response can also be capped at seven days.
HttpOnlydoes not prevent this cap.
WebKit also documents an IP heuristic. The version described in 2024 considers IPv4/IPv6 address families and shared address prefixes, among other details. Such heuristics can change; they do not establish a permanent recipe for unlimited persistence.
3. Consequences for measurement
If an analytics identifier disappears, a later visit may appear as a new browser. Earlier contacts may no longer connect to a conversion. The extent and direction of distortion nevertheless depend on the system, available identifiers and attribution model.
An eight-day absence therefore does not inevitably generate a new ID in every configuration. Nor do all cohorts or A/B tests automatically lose statistical usefulness. Comparing Safari with Chrome can suggest a problem but cannot isolate its cause: devices, campaigns, consent and behaviour may differ too.
4. Understanding operator-controlled endpoints and attributes
A reverse proxy on the same host can provide a controlled data path. A CDN may terminate TLS without its IP addresses belonging to the website operator. Same origin, same site and organisational control are distinct concepts.
HttpOnly prevents JavaScript access to a cookie. Secure restricts transmission to HTTPS, while SameSite affects cross-site requests. None guarantees a particular lifetime. A server can also set a cookie without HttpOnly; the actual Set-Cookie response establishes the setting path.
Legitimate sessions and permitted measurement need purpose-appropriate identifiers, suitable retention and consent where required. An operator-controlled domain neither establishes permission to track nor makes tracking immune to browser protection. On 19 October 2026, WebKit additionally described domain-level blocking of identity-resolution infrastructure in operating-system releases 27. This network measure is separate from cookie time limits.
5. Assessing a specific installation
- Record Safari and operating-system versions, regular or private browsing and relevant protection settings.
- Document the hostnames and DNS resolution of the main document and measurement endpoint.
- Use Web Inspector to identify the cookie-setting response or script operation. Compare attributes with the expiry actually stored.
- Treat return visits, interaction, existing consent and cookie renewal as separate test cases.
- Distinguish missing identifiers, blocked requests and business events. One page load does not establish persistence over several days.
Questions and answers
Does a click ID alone trigger the 24-hour limit?
The documented rule combines navigation origin, classification, URL and JavaScript setting. A list of parameter names cannot replace that assessment.
Are CDNs and same-origin proxies always exempt?
The CNAME rule also considers the main document’s CNAME. A CDN serving the entire website therefore differs from a separately delegated tracking subdomain. This does not establish a general exemption from every protection mechanism.
Does Google Tag Gateway guarantee persistent cookies?
A path on the website host initially describes routing. The cookie’s JavaScript or HTTP setting method and applicable rules need separate examination. Neither the product name nor the presence of HttpOnly proves lasting measurement continuity.
Related articles